The End of iptables in Kubernetes: eBPF and Gateway API Become the Default
Eliminating O(N) firewall bottlenecks as eBPF and Kubernetes Gateway API standardize cloud networking; why platform teams are shifting traffic routing from user-space to the Linux kernel.
Source Reference: [Cloud Native Computing Networking Architecture Releases] · Reviewed Date: 2026-11-05
Confirmed Industry Shift
Enterprise cloud-native networking has officially transitioned beyond legacy iptables and kube-proxy architectures. With modern CNIs maturing and Kubernetes Gateway API reaching production status, eBPF-driven data paths have become the de facto standard. Modern network engines now process filtering, NAT, and Layer 4–7 authentication directly within the Linux kernel socket layer.
Editorial Analysis
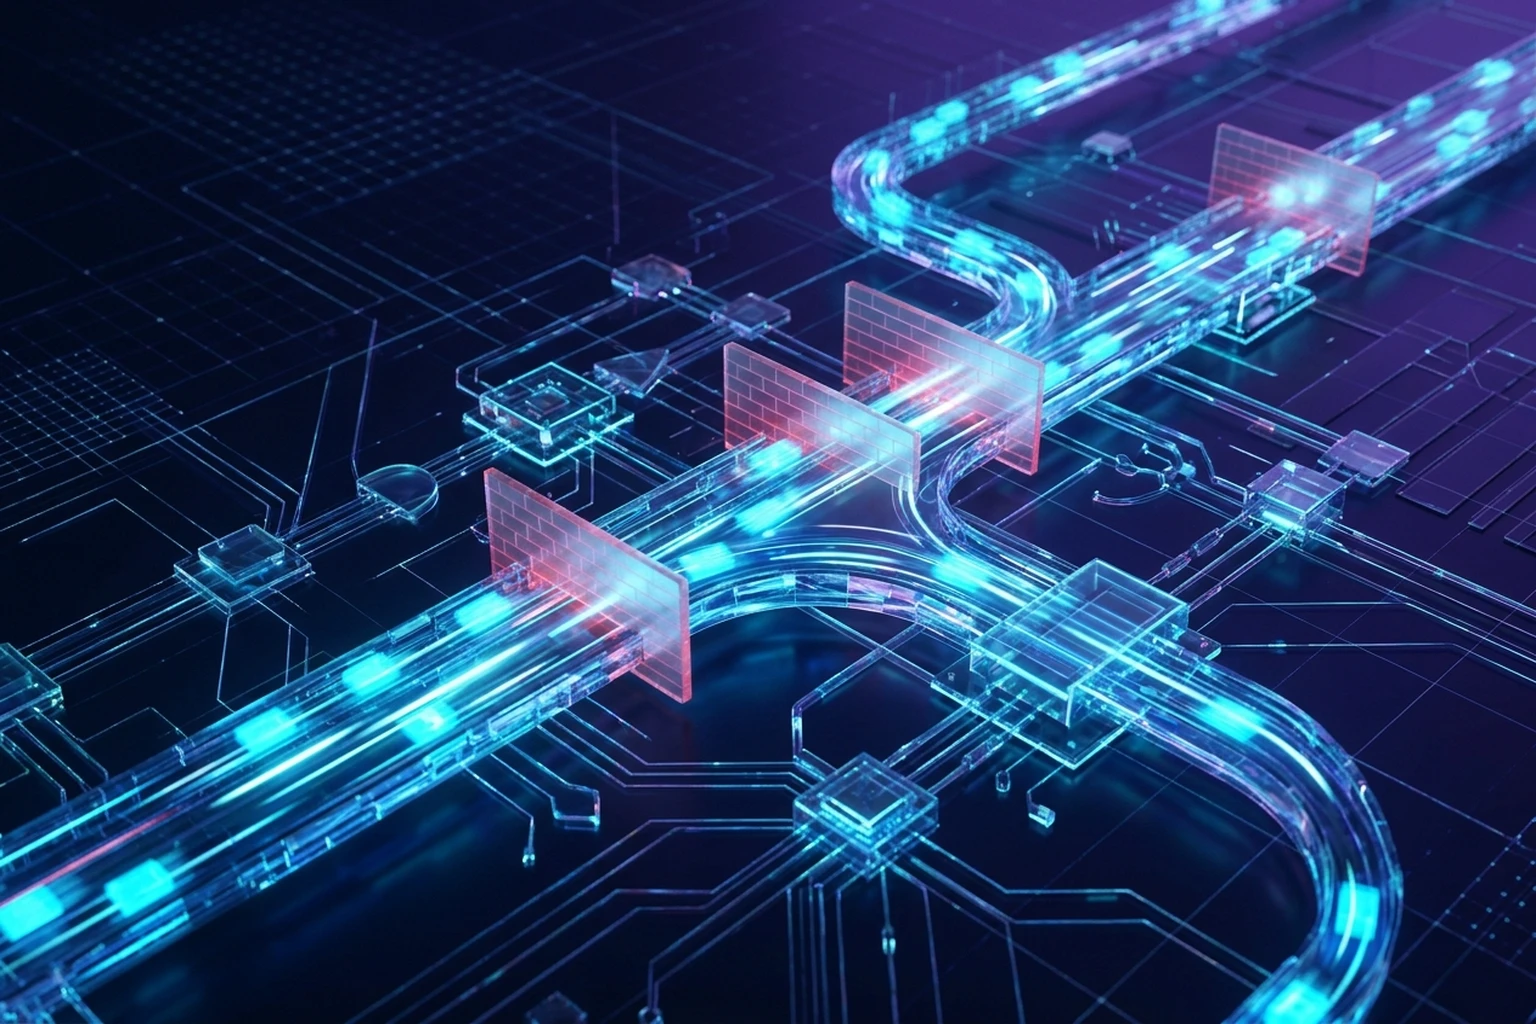
For over a decade, standard container networking relied on sequential iptables packet evaluations. As clusters scaled to thousands of microservices, the linear $O(N)$ rule evaluation introduced severe latency jitter and high CPU overhead. Each incoming packet traversed hundreds of rules sequentially.
By leveraging eBPF hash maps with constant $O(1)$ lookup complexity, network throughput remains deterministic regardless of cluster scale. Furthermore, tight integration with the Gateway API enables sophisticated cross-namespace traffic splitting and zero-trust policy enforcement without injecting resource-heavy sidecar proxies (Sidecarless architecture).
Our assessment is that this shift removes proxy maintenance burdens from platform teams while strengthening kernel-level observability.
Pre-Adoption Considerations
- Verify host Linux kernel version (version 5.10+ is mandatory for advanced eBPF maps and socket layer programs).
- Re-architect observability pipelines; traditional firewall inspection commands like
iptables -Lno longer capture eBPF traffic. - Conduct chaos experiments on kernel bypass fallbacks.
Practical Takeaway
Persisting with legacy user-space routing stacks incurs silent latency penalties and waste computing overhead. Migrating cluster data paths to eBPF and the Gateway API represents a vital optimization for modern platform reliability.
Continue reading
All posts →
Large Packets Dropped: Resolving MTU Mismatch and PMTU Black Holes
Troubleshooting stalled SSH sessions, failing SCP file transfers, and frozen TLS handshakes over VXLAN, WireGuard, and GRE tunnels; enforcing MSS clamping instead of arbitrary NIC edits.
Mandatory Kubernetes Migration to cgroup v2: Beyond a Kernel Parameter
A production runbook for migrating Kubernetes clusters to cgroup v2; troubleshooting failCgroupV1, Pressure Stall Information (PSI), resolving Java OOMKilled regressions, and zero-downtime node upgrades.

SMB access denied: do not grant Everyone full control
Restore SMB access after permission changes by distinguishing share and NTFS rights, making a narrow correction and testing as the actual user.